This page answers procurement's questions so your engineers don't have to ask them. It covers data ownership in one sentence, the security mechanisms we run, the standards we are certified to, and how the AI is bounded. We apply the same standard to our forecast numbers.
You own your raw telemetry and everything derived from it for your plant. DYNVOLT owns its trained models.
In practice: your inverter, string, meter and sensor data, your forecasts, your reports and your work-order history are yours: exportable at any time and portable if you leave. DYNVOLT retains ownership of its model architectures, trained model weights, and aggregated, anonymised learnings across the fleet. The contract draws that line in those words, so it never has to be settled in a dispute.
Our information security management system is certified to ISO/IEC 27001:2022 and our quality management system to ISO 9001:2015. The posture below is concrete and auditable today. Ask us to demonstrate any line of it.
Edge gateways accept no inbound connections. All connectivity is outbound encrypted tunnels; administrative access runs over a private mesh network instead of an exposed port. No port is opened on the plant network for inbound connections.
Configuration and secrets arrive in signed envelopes the edge verifies before applying. OS packages come from a GPG-signed repository; application images are CI-built.
One identity provider for every surface: offline-verifiable tokens, TOTP step-up for sensitive actions, machine-to-machine credentials scoped per service.
Audit records are hash-chained, so an edited or deleted record breaks the chain when it is verified. Every plant-control write also lands in a per-write command log with the actor, role and context. Our own forecast audit used that log to find and exclude curtailment days.
Connectivity loss never becomes a control gap: polling, alarms and the export limit keep running at the edge, and the cloud catches up from the local buffer, which holds months of data, when the link returns.
The AI operator reads everything and changes nothing by default. Write access is off until you switch it on for a site, and even then it can do exactly two things: set a power limit and acknowledge an alert. Each one arrives as a proposal that a named person confirms or declines in Telegram or on the dashboard.
A confirmed action runs through the SCADA's own audited command endpoint, under the operator's service account, so it shows up in the same command log as every human write. The operator cannot place bids and cannot create work orders. Market actions on the trader desk are suggestions a trader approves.
DYNVOLT is certified by TÜV NORD CERT to ISO/IEC 27001:2022 (information security) and ISO 9001:2015 (quality management). Certification to ISO/IEC 20000-1 (IT service management) is under way. See the certificates.
Energy operators fall inside NIS2 scope, which makes DYNVOLT part of your supply chain. We support your obligations with the mechanisms above, documentation of our architecture, and evidence on request.
Your data is exportable at any time in open formats, and source-code escrow is available on request. The edge runs the plant's monitoring, alarms and export limit on site, so the plant never depends on a connection to keep within its permit.
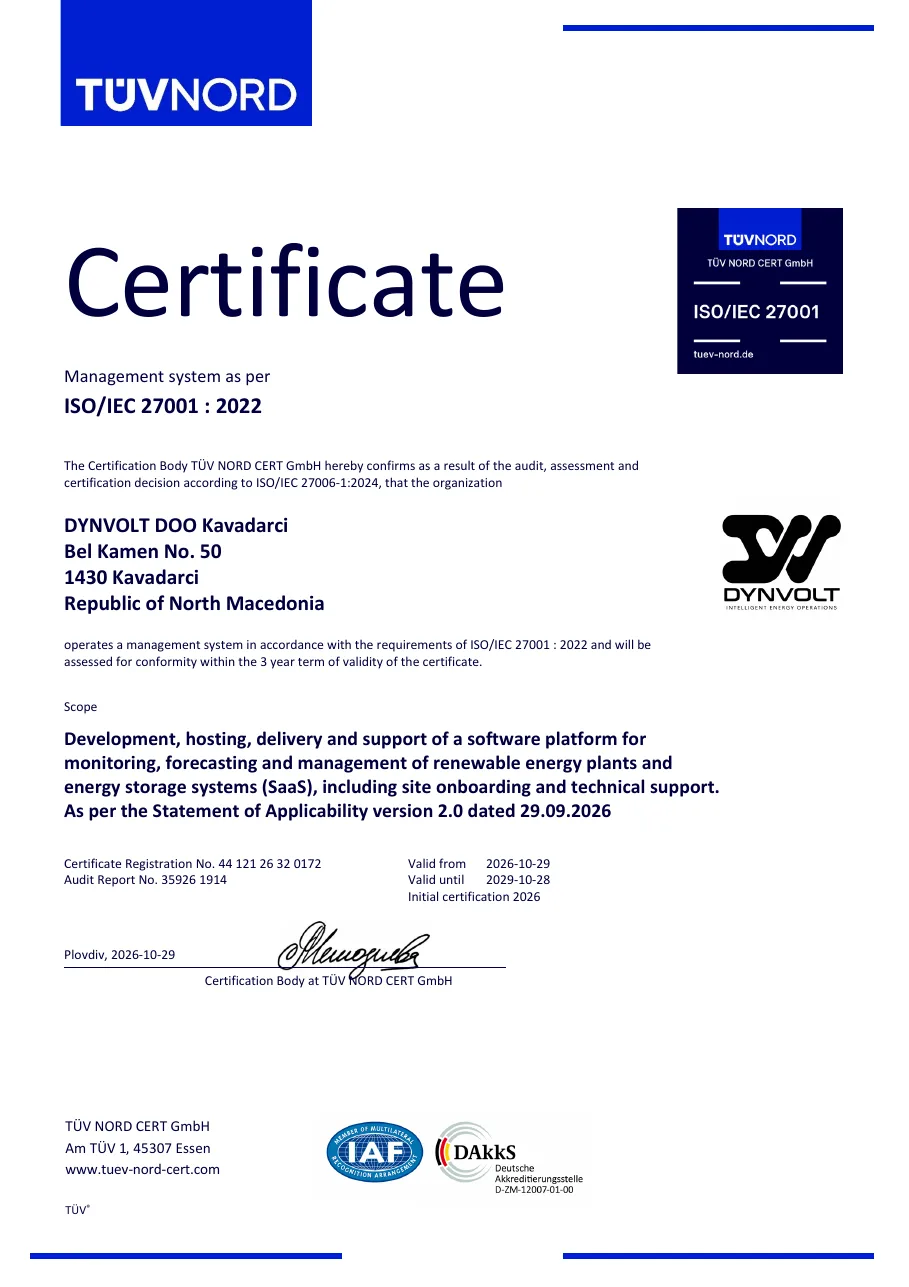
TÜV NORD CERT audited and certified our information security management system for the same service: the platform, its hosting, and the people and processes that operate it for your plants.


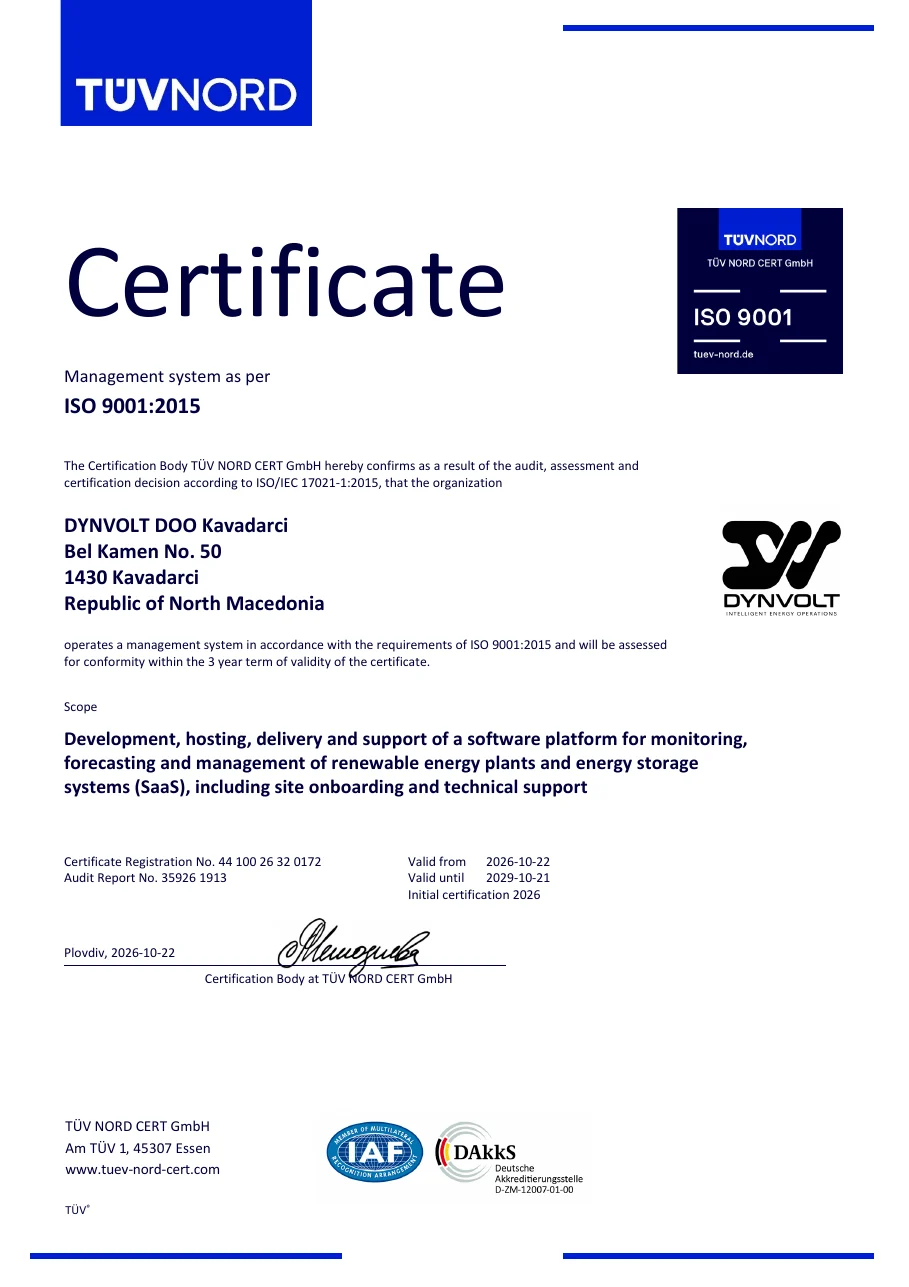
TÜV NORD CERT audited and certified our quality management system for the whole service we deliver, from building the platform to running it for your plants.

DYNVOLT DOO Kavadarci
Bel Kamen 50, Kavadarci, North Macedonia
Registration number: 7957653 · Tax ID: 4011026526422
admin@dynvolt.com
The same entity appears in our terms, privacy policy, and on your contract.
Walk through the security architecture, the data-ownership contract language, and the escrow terms on a call with the people who built it.